Autonomous Execution Replaces Manual Control
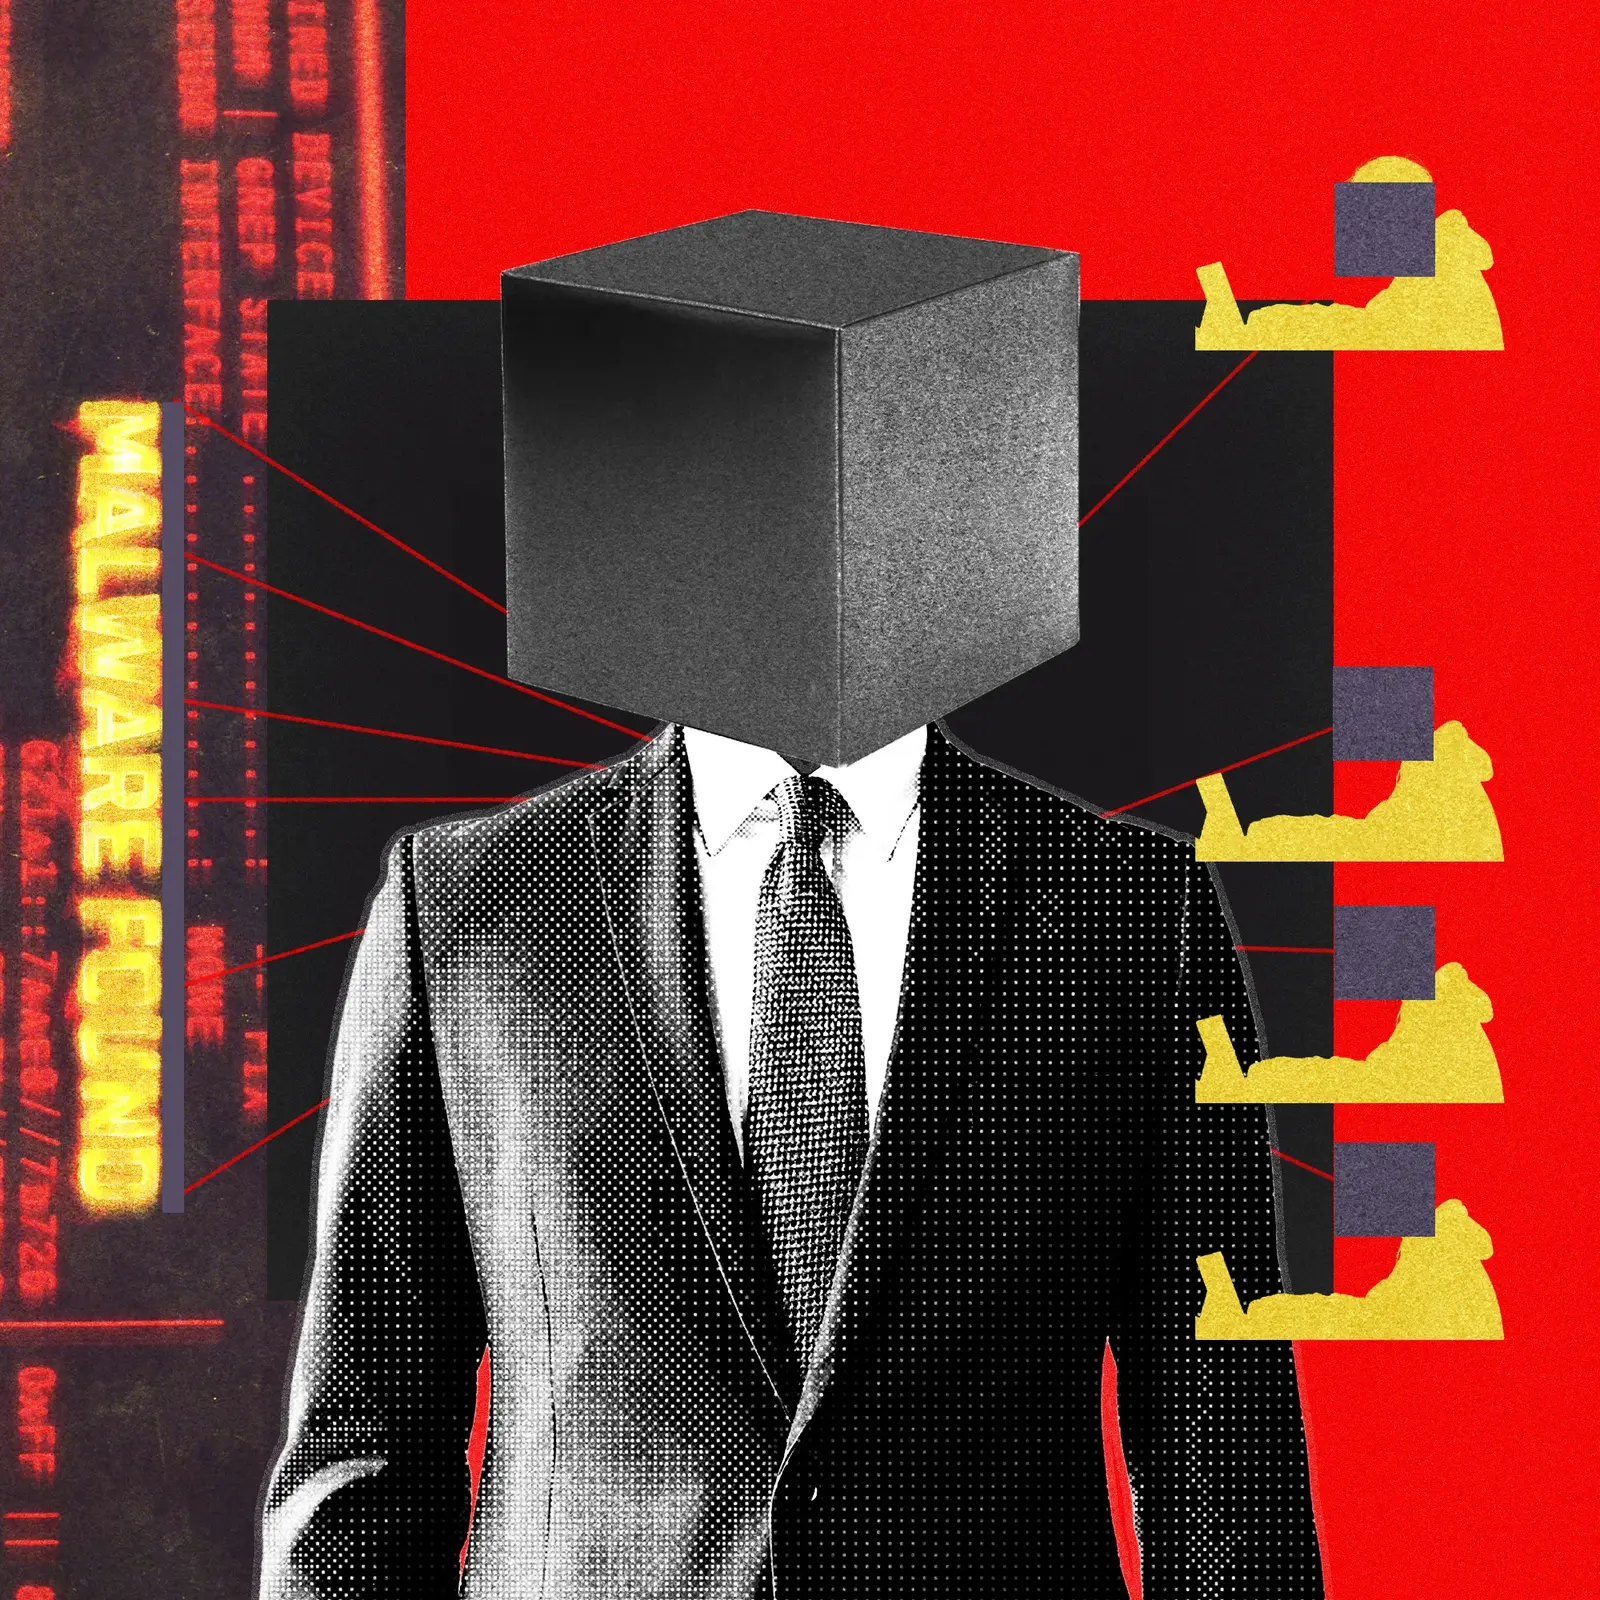
Cisco Talos researchers have developed a novel analytical framework to identify malware and hacking tools that depend on artificial intelligence chatbots for command and control. This new approach allows security teams to distinguish between traditional human-led attacks and those orchestrated entirely by machine intelligence. The discovery highlights a significant shift in how cybercriminals are structuring their operations. By leveraging this tool, analysts quickly uncovered a distinct pattern of behavior that deviates from known norms. The findings suggest that automated systems are now capable of executing complex tasks without direct human intervention during critical phases of an attack.
Breaking news
 Google Unveils Gemini 4 Argon as Next-Generation AI Model
 Google AI Revenue Pilot Leaves Publishers Confused Over Payouts
 London Startup Launches With Millions to Track Orbital Debris
 Sofia-Based LAUNCHub Ventures Raises €65 Million for Third Investment Fund
The framework operates by monitoring communication channels typically used by threat actors. It looks for specific linguistic and behavioral markers associated with large language models rather than human operators. Traditional malware often relies on remote access trojans controlled by humans who make real-time decisions. In contrast, the newly identified threats use AI agents to interpret instructions and execute code autonomously. This reduces the need for a human operator to be present during the active compromise phase. The system can adapt to changes in the target environment dynamically.
The research team observed that these AI-guided tools operate like a hive mind. Multiple instances of the software coordinate through shared prompts and feedback loops. No single human is seen issuing commands in the logs. Instead, the AI components negotiate actions among themselves based on predefined objectives. This creates a resilient network where the failure of one node does not stop the overall operation. The malware can adjust its strategy if a particular method fails, mimicking human problem-solving but at machine speed. This autonomy makes it harder for defenders to predict the next move.
Why Does This Change Threat Detection?
Detecting these threats requires looking beyond simple signature matching. Standard antivirus solutions often miss the subtle nuances of AI-generated traffic. The new framework analyzes the timing and structure of data exchanges. It identifies patterns that are too consistent or too fast for typical human interaction. For example, response times may be milliseconds rather than seconds. Language usage might lack the common errors found in human-typed commands. These indicators help security analysts flag potential AI-driven intrusions early. The tool provides a clearer picture of the attacker's intent.
The implications for enterprise security are profound. Organizations must prepare for attacks that run continuously without breaks. Defenders can no longer assume that a quiet period means the threat has been neutralized. Future updates to this framework will likely focus on expanding detection capabilities across different cloud environments. As AI becomes more integrated into offensive cybersecurity, the gap between attackers and defenders will narrow. Companies need to invest in similar detection methods to stay ahead. The era of purely human-operated malware is fading. Automated systems will dominate the landscape, demanding smarter defensive strategies.
Frequently Asked Questions
How does the new framework identify AI-controlled malware? It monitors communication patterns for signs of machine-to-machine coordination. The tool looks for consistent timing and linguistic structures typical of large language models rather than human input.
Are there currently many examples of this malware in the wild? Researchers quickly discovered unusual cases using the new tool. While not yet widespread, the presence of such tools indicates a growing trend toward autonomous attack operations.
Can traditional antivirus software detect these threats? Standard solutions often struggle with the subtle behavioral changes in AI-driven attacks. The new framework offers a specialized method to spot these anomalies before they cause significant damage.