Concurrent Processing Triggers Memory Corruption
A high-severity use-after-free vulnerability has been identified in the Linux kernel. The flaw specifically targets the IPv4 TCP handshake process. It affects systems where multiple processors handle network connections simultaneously. The issue arises during the creation of child sockets. This critical bug allows for memory corruption under specific concurrent conditions. Security researchers have assigned it the identifier CVE-2026-98432. The vulnerability poses a significant threat to server stability.
Breaking news
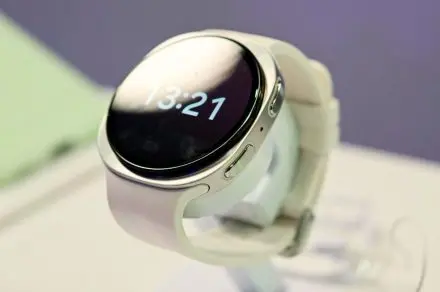 Samsung Shifts Galaxy Watch Strategy to Two-Year Release Cycle
 Tesla rolls out FSD v15 with major safety upgrade
 Open-Source Tools Challenge AI-Powered Development Platforms
 AI Infrastructure Bottlenecks: Why Release Pipelines Hold Back Fast Clusters
The core problem lies in how the kernel manages IP options objects. During a TCP connection setup, request and child sockets may share this object. If two CPUs process these sockets at the same time, a race condition occurs. One processor might free the shared memory object immediately. Meanwhile, another processor, acting as an RCU reader, continues to access it. This creates a dangerous window where invalid memory is referenced. The result is a classic use-after-free error. This type of bug can lead to system crashes or potential privilege escalation.
The vulnerability exploits the complexity of multi-core networking. Modern servers rely on parallel processing to handle high traffic volumes. In this context, the kernel’s reference counting mechanism fails to protect the IP options structure. The RCU (Read-Copy-Update) mechanism provides protection for readers but not against immediate freeing by writers. When the writer frees the object, the reader’s pointer becomes stale. Accessing this stale pointer leads to undefined behavior. Attackers could potentially leverage this to execute arbitrary code. The flaw is subtle but dangerous in high-load environments. It highlights the challenges of maintaining memory safety in complex kernel code.
How Can Administrators Mitigate This Threat?
System administrators must apply the latest kernel patches immediately. The fix ensures proper synchronization between the request and child socket paths. It prevents the premature freeing of the IP options object. Until patches are deployed, reducing concurrent TCP connection establishment may help. However, this is not a complete solution. Monitoring for unusual kernel panics or memory errors is recommended. Organizations should prioritize this update for internet-facing servers. The bug does not require user interaction to trigger. It can be exploited remotely by sending specific network packets. This makes it a critical priority for infrastructure security teams.
The discovery of CVE-2026-98432 underscores the ongoing need for rigorous kernel auditing. As networking hardware becomes more powerful, concurrency bugs become more prevalent. Security teams must remain vigilant against similar flaws in future releases. The patch validation process confirms that the fix resolves the race condition. Users should verify their kernel versions against the advisory. Failure to update leaves systems exposed to potential denial-of-service attacks. The broader implication is a reminder that low-level code requires constant scrutiny. Future kernel versions must incorporate stricter memory safety checks. This incident serves as a wake-up call for the open-source community.
Frequently Asked Questions
What is the primary impact of CVE-2026-98432? The flaw causes a use-after-free error during TCP handshakes. This can lead to system instability or remote code execution.
Which systems are most at risk? Multi-core Linux servers handling high volumes of concurrent TCP connections are most vulnerable. Single-threaded systems are less likely to trigger the race condition.
How should users respond to this vulnerability? Apply the latest kernel update immediately to patch the memory management bug. Verify the patch installation and monitor system logs for errors.